STORM Platform · Continuous Monitoring

Turn cloud configuration into continuous evidence.

Continuously validate cloud security configurations, evaluate device, identity and security posture, map technical checks to frameworks and reuse applicable results in compliance assessments.

Connectors cover Microsoft cloud, identity and device services, AWS, Google Cloud, Jamf and CrowdStrike. Connector permissions and licensing are confirmed for each deployment.

Configuration monitoringSources connected
Check
Technical posture in compliance context

Configuration data becomes evaluated control status, framework coverage, historical results and reusable evidence.

EntraIdentity
IntuneDevices
DefenderSecurity
M365Cloud
MFA enforcement checkThreshold · severity · framework coverage
Evaluated
Device encryption checkCurrent state · implementation status · last detected
Visible
ConnectorsCollect configuration data from cloud, identity, device and endpoint tools.
Checks catalogEvaluate posture through predefined technical checks.
Framework mappedConnect technical checks with ISO/IEC 27001 and supported frameworks.
Evidence reusedPopulate applicable compliance responses from configuration data.
From point-in-time to operational

See configuration change before the next assessment cycle.

Manual attestations age quickly when identity, device and cloud settings keep changing. STORM connects configuration data from your security stack with a governed check catalog, evaluation logic, framework mappings and assessment evidence so technical posture can be reviewed in the same context as compliance.

01 · COLLECT

Connect configuration

Use connectors for Microsoft, AWS, Google Cloud, Jamf and CrowdStrike to retrieve device, identity, cloud and endpoint data.

02 · EVALUATE

Run technical checks

Apply predefined checks with configurable thresholds, grace periods and severity.

03 · MAP

Add framework context

Show which supported framework controls each technical check covers.

04 · EVIDENCE

Reuse the result

Feed applicable evaluated data into the Compliance Assessment workflow.

Inside the platform

Technical checks that stay connected to compliance.

The workflow combines connector-based data collection, configurable validation, historical visibility, framework mapping and automated evidence.

01 · Checks catalog

Make the validation logic visible.

Use a library of predefined technical security configuration checks. Each catalog entry can expose its subject, severity, evaluation thresholds, grace period, framework coverage, current state, implementation status and last-detected context.
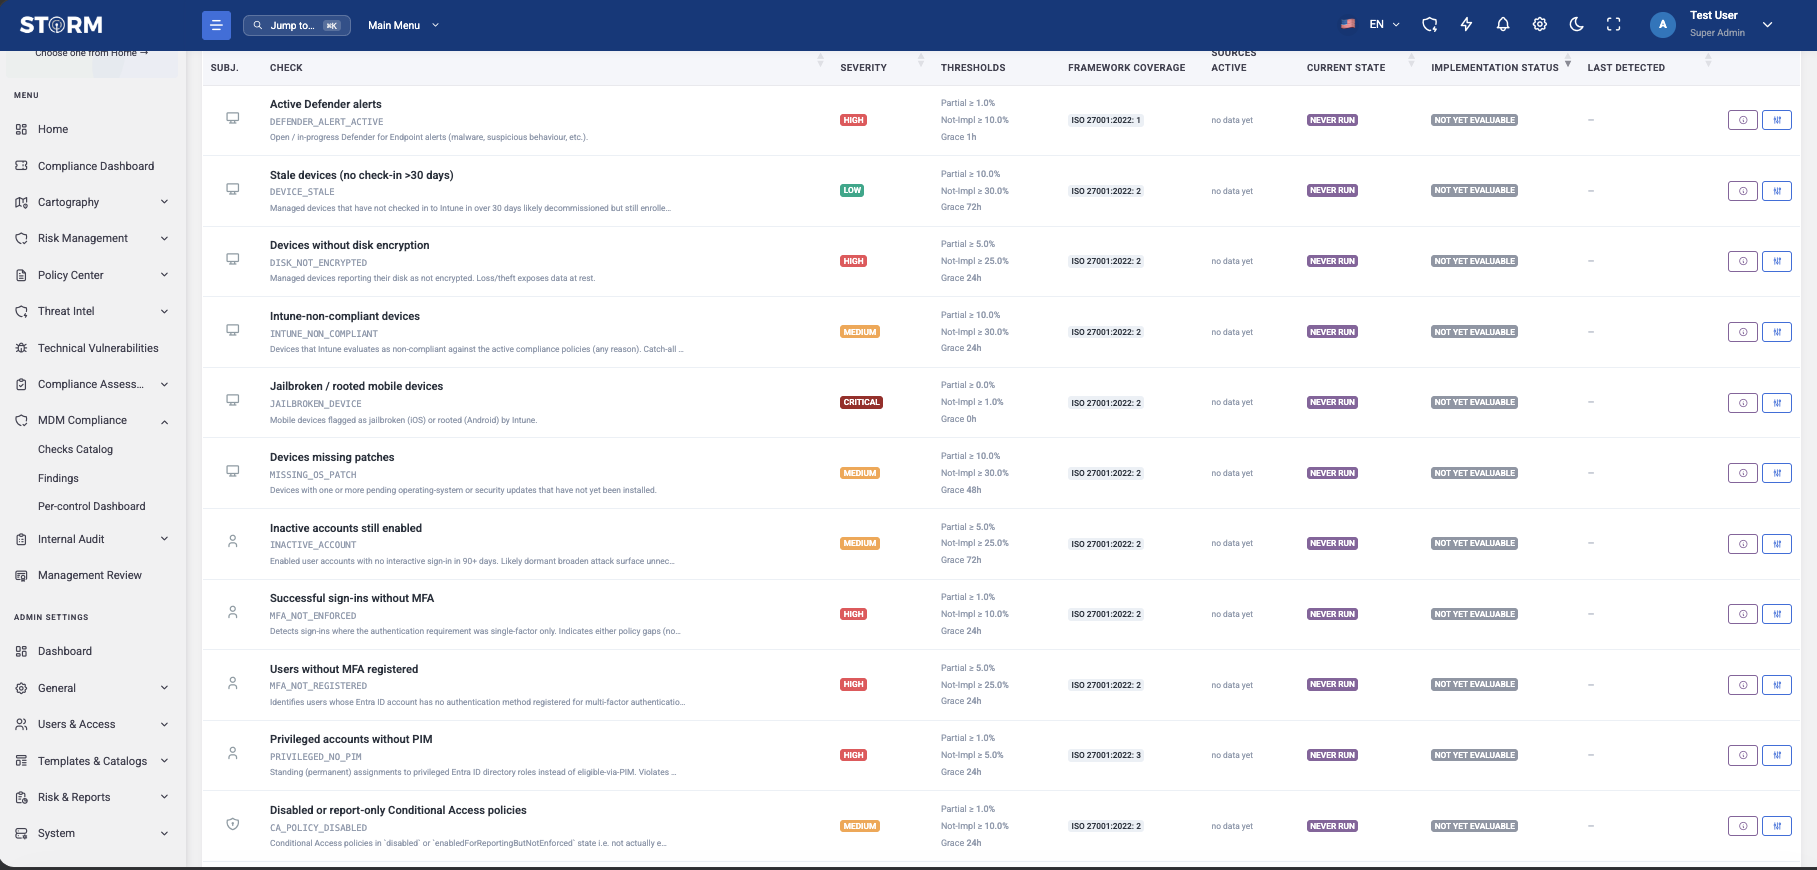
  • Predefined technical configuration checks
  • Severity, thresholds and grace periods
  • Framework coverage and execution history
STORM Checks Catalog showing security checks, severity, thresholds, framework coverage, state and implementation status
02 · Configuration data

Bring identity, device and security settings into one validation layer.

Connectors collect security configuration data from Microsoft Entra ID, Intune, Defender, Azure, Sentinel and Microsoft 365, plus AWS, Google Cloud, Jamf and CrowdStrike, for continuous device, identity, cloud and endpoint posture checks.

  • Microsoft Graph API and third-party connectors
  • Cloud, identity, device and endpoint sources
  • Automatic control implementation-status evaluation
Documented current integrationConfiguration data → evaluated check
03 · Configurable evaluation

Apply thresholds that reflect the control intent.

Configure compliance thresholds, grace periods and severity for each technical control. STORM automatically evaluates implementation status and retains historical execution results and last-detection context for review.

  • Configurable partial and non-implementation thresholds
  • Grace-period and severity settings
  • Historical results and last-detection tracking
01
Define the checkSource, subject and expected technical state
Logic
02
Apply evaluation rulesThreshold, grace period and severity
Evaluate
03
Retain the outcomeStatus, execution history and last detection
History
Continuous validation modelCheck → evaluate → retain
04 · Framework mapping and evidence

Reuse technical truth inside the assessment.

Map technical checks to relevant ISO/IEC 27001 controls and other supported frameworks, show coverage for each check, and use evaluated configuration data as an evidence source for applicable Compliance Assessment responses.

  • Technical-check to framework-control mapping
  • Framework coverage visibility
  • Automated evidence and applicable response pre-population
Connected evidence workflowTechnical result → compliance context
05 · Objectives and KPIs

Monitor technical controls and management objectives in one rhythm.

The documented ISMS Objectives & KPIs module adds measurable objectives, one or more indicators, owners, target periods, units and performance thresholds. KPI values may be recorded manually or collected automatically where integrations are available.
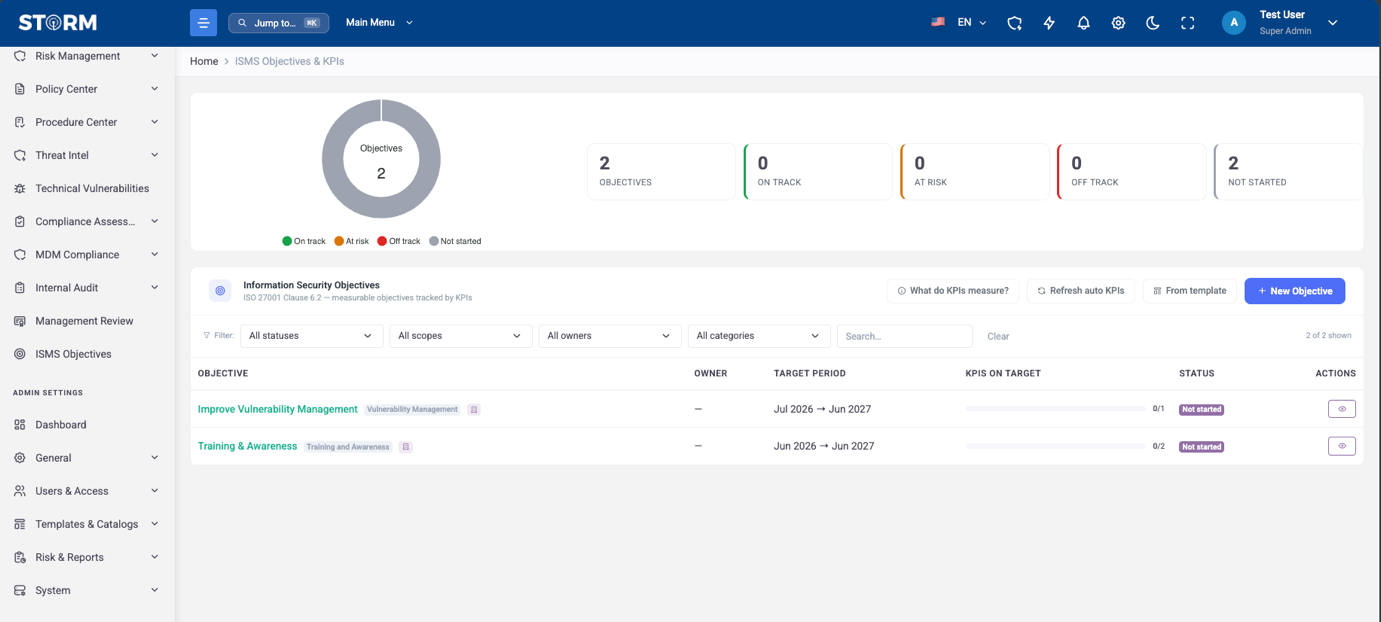
  • Custom objectives, KPI targets and owners
  • Manual and integration-dependent automated values
  • Historical trends and management reporting
STORM ISMS Objectives and KPIs dashboard showing objective status, owners, periods and KPI progress
From configuration to evidence

Keep the technical signal connected and reviewable.

STORM preserves the path from source configuration through evaluation and framework mapping to the evidence used in compliance oversight.

01

Connect

Source connectors

02

Collect

Security configuration data

03

Evaluate

Thresholds and severity

04

Map

Framework control coverage

05

Evidence

Applicable assessment response

06

Review

History, dashboards and KPIs

Integrations

Your security stack, continuously checked.

STORM continuously validates cloud security configurations and monitors device, identity and security posture against predefined controls.

Each technical check maps to ISO 27001 and other supported frameworks, so live compliance evidence is ready for your assessments.

Cloud security
  • Microsoft Azure
  • Amazon Web Services (AWS)
  • Google Cloud (GCP)
Identity security
  • Microsoft Entra ID
  • Conditional Access
Device management
  • Microsoft Intune
  • Jamf
Endpoint security
  • Microsoft Defender
  • CrowdStrike
Collaboration
  • Microsoft 365
SIEM
  • Microsoft Sentinel

What each connector shows

Azure

Cloud security

of 23 evaluated checks passing

Passing
14
Failing
9
Not evaluated
37

24 open findings 16 high

Top failing checks

  • Applicable Defender for Cloud plan disabled10
  • JIT access missing for exposed management ports3
  • Defender security recommendations unresolved1
  • +6 more failing

Evaluated 11 Oct 2026, 07:17

CrowdStrike

Endpoint security

of 7 evaluated checks passing

Passing
2
Failing
5
Not evaluated
3

66 open findings 1 critical33 high

Top failing checks

  • Open Falcon detections (high/critical)22
  • Endpoint has no Falcon sensor11
  • Falcon host in Reduced Functionality Mode1
  • +2 more failing

Evaluated 11 Oct 2026, 07:18

Entra ID

Identity security

of 4 evaluated checks passing

Passing
2
Failing
2
Not evaluated
0

88 open findings 1 critical2 high

Top failing checks

  • Users without MFA registered3
  • Inactive accounts still enabled85

Evaluated 11 Oct 2026, 08:01

Intune

Device management

of 5 evaluated checks passing

Passing
3
Failing
2
Not evaluated
0

22 open findings

Top failing checks

  • Intune non-compliant devices2
  • Stale devices (no check-in >30 days)20

Evaluated 11 Oct 2026, 08:01

Key capabilities

  • Automated collection of security configuration data from Microsoft Entra ID, Microsoft Intune, Microsoft Defender, Microsoft Azure, Microsoft Sentinel and Microsoft 365, as well as AWS, Google Cloud, Jamf and CrowdStrike
  • Library of predefined technical security configuration checks
  • Continuous monitoring of device, identity and security compliance posture
  • Configurable compliance thresholds, grace periods and severity levels for each technical control
  • Automatic evaluation of control implementation status
  • Mapping of technical checks to ISO 27001 controls and other supported compliance frameworks
  • Framework coverage visibility for each automated check
  • Dashboard showing current compliance status and technical configuration health
  • Automated evidence generation to support compliance assessments
  • Integration with the Compliance Assessment module to populate applicable framework controls automatically
Practical questions

Validate the workflow with a real configuration check.

Bring one representative control, its source, threshold logic, framework mapping and expected assessment response to the walkthrough.

Which systems can STORM monitor?
Microsoft Entra ID, Microsoft Intune, Microsoft Defender, Microsoft Azure, Microsoft Sentinel and Microsoft 365 through the Microsoft Graph API, plus AWS, Google Cloud, Jamf and CrowdStrike. Connected accounts, permissions and check coverage are confirmed for each deployment.
What does “continuous” mean in STORM?
The product description states continuous automated configuration validation and monitoring. It does not publish a universal execution interval, so the exact schedule and refresh behaviour should be confirmed for the intended deployment.
Can each technical check have its own evaluation rules?
Yes. Configurable compliance thresholds, grace periods and severity levels are documented for each technical control, together with automatic implementation-status evaluation.
Does STORM automatically change a failing configuration?
Automated configuration enforcement or autonomous remediation is not documented. The stated capability is collection, validation, status evaluation, monitoring and evidence generation.
Can technical results support compliance assessments?
Yes. STORM documents automated evidence generation and integration with Compliance Assessment to pre-populate applicable framework-control responses from live configuration data.
Which frameworks can technical checks map to?
ISO/IEC 27001 mapping is explicitly documented, together with mappings to other supported compliance frameworks. The exact additional framework coverage should be reviewed in the check catalog for the intended deployment.
Are historical results retained?
Yes. Historical execution results and last-detection tracking are documented, along with dashboards for current compliance status and technical configuration health.
Does Continuous Monitoring include objectives and KPIs?
STORM has a documented ISMS Objectives & KPIs module for objectives, indicators, targets, thresholds, owners, periods and historical trends. KPI values can be manual or automated where a supporting integration is available.

Bring one security control and its expected state.

Validate collection, check logic, implementation status, history, framework mapping and assessment evidence against the environment your teams operate.

Book a STORM demo
Certifications

ICT PROTECT, the company behind STORM GRC, holds internationally recognised certifications and independent assurance.

View all certifications
  • CERTIFIED ISO 27001
  • CERTIFIED ISO 22301
  • CERTIFIED ISO 9001
  • CERTIFIED CYBER ESSENTIALS
  • CERTIFIED CYBER ESSENTIALS PLUS
  • ASSURANCE ISAE 3000 TYPE II

The certifications and assurance reports shown here are held by ICT PROTECT and apply within their stated scope, which includes the STORM GRC platform.